RSA Authenticator (SecurID)
by RSA Security
3.3
- Safety
- 100% Safe
- Category
- Communication
- Ratings
- 3.3
- Price
- Free
- Download
- 10.00M
This app is secure, reliable, free to install, and offers fast downloads without any risks or malware.
Screenshots
 Analysis by Getfullapps
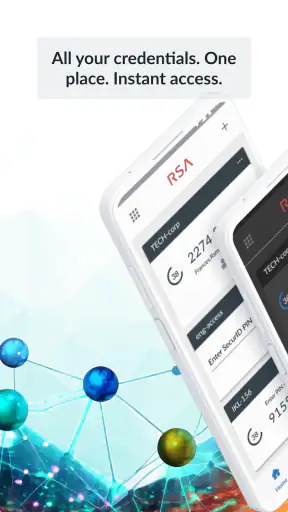
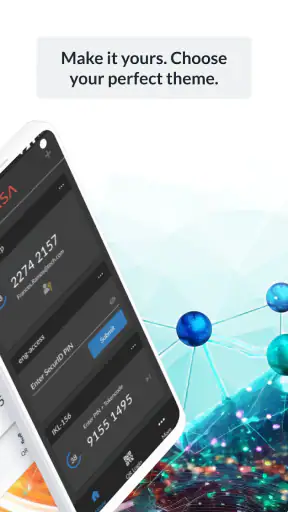
I found RSA Authenticator (SecurID) most useful as a focused security key rather than a general communication app. It is designed to help me prove my identity when a service asks for an extra verification step, using options such as passkeys, biometrics, and one-time passwords. That narrow purpose is also its biggest strength: once an organization has configured it for me, the app can turn a potentially awkward sign-in into a quick approval or code entry.
My overall view is positive but practical. I would recommend it to people whose workplace, school, bank, or other managed service already relies on RSA Security. I would not install it simply because I want a spare authenticator for every personal account. In that situation, another authenticator may feel easier to set up and more flexible. RSA Authenticator makes the most sense when it is part of an existing identity system, not when I am choosing a security app in isolation.
What the app does well in everyday sign-ins
The app comes from RSA Security and sits in the communication category, although its real role is authentication. The store summary describes support for passkeys, biometrics, OTP, and more, and that combination gives it a broader job than a basic code generator. Instead of treating every login as a manual copy-and-paste task, it can support different ways of confirming that I am the person behind the account.
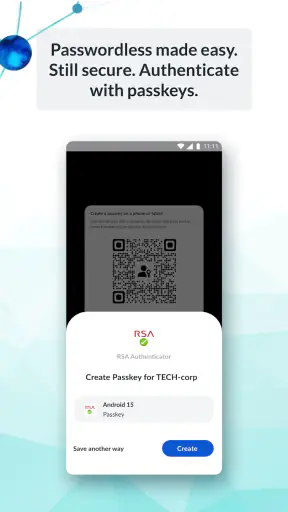
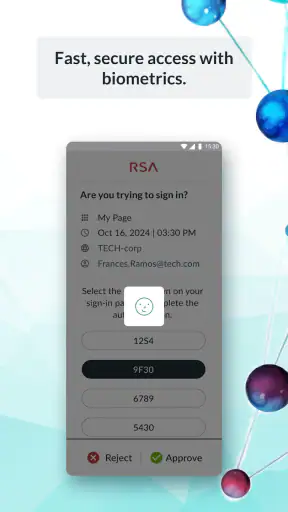
In daily use, the most valuable improvement is reducing the number of steps between opening a service and getting access. A one-time password can be entered when a login screen asks for it, while biometric confirmation can make the approval feel more natural on a compatible device. Passkeys are especially appealing for people who dislike typing codes, because the phone can handle more of the identity check without asking me to remember another secret.
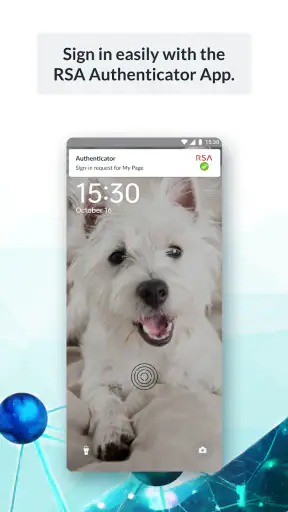
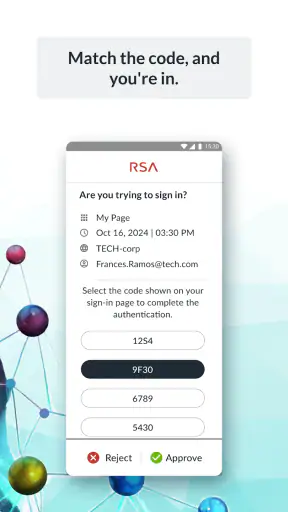
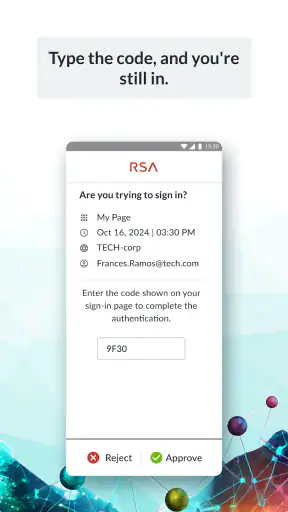
A realistic example is a workday morning. I open a company service from my phone or computer, enter my normal credentials, and reach the additional verification stage. Rather than searching through messages or waiting for a text, I open the authenticator and complete the method my organization has enabled. If the account uses a code, I copy the current code before it changes. If it uses a biometric or passkey flow, I can finish with the phone’s own security check. The benefit is not dramatic every time, but it becomes noticeable when I sign in repeatedly during a busy day.
That workflow also reveals an important detail: this is not an app I can fully judge by its icon and first launch screen. Much of the experience depends on how the organization has set up RSA authentication. One user may see a clean biometric or passkey process, while another may mainly use OTP codes. The app is therefore best understood as a client for a broader security arrangement, not as a standalone service that creates value without an account or enrollment process.
I also appreciate that the app supports more than one authentication style. If a service allows several methods, I can choose the one that fits the moment. Biometrics are convenient when the phone is already in my hand. A passkey can be preferable when I want to avoid manually reading a changing code. OTP remains useful when compatibility matters or when a service has not moved to a newer sign-in method.
Articles to Explore Next

Uber Eats Makes Dinner Easier to Manage, but the Fees Add Up

Google Photos Turns a Camera Roll Into a Library You Can Find Your Way Through

Canva on Mobile: Adopt It for Quick Visuals, Test It for Demanding Work

Google Drive Keeps Work Moving Until It Doesn’t

Switching to Weather - By Xiaomi Means Relearning Your Forecast Routine

Ludo King and the Social Life of a Lucky Six
The strongest reason to use RSA Authenticator is its ability to bring several verification methods into one organization-managed sign-in experience. That matters more to me than visual polish. Security tools should make the safe action easier, and this app can do that when the setup behind it is configured properly.
Enrollment is where patience matters
The first setup is not necessarily as immediate as installing a casual utility. I need the relevant account or enrollment instructions before the app can become useful. In a workplace environment, that may mean following an administrator’s process. If I install the app before I have those details, I should not expect it to discover all of my accounts automatically or work as a universal replacement for every login method.
My practical advice is to complete enrollment when I have reliable access to both the service I am protecting and the phone I will use for verification. I would avoid starting the process while traveling, rushing into a meeting, or switching between devices. Authentication setup is the wrong place to improvise, because a half-finished registration can leave me unsure which method is active.
I would also test the sign-in flow immediately after enrollment, while the support contact or administrator is still easy to reach. That test answers useful questions: whether the prompt arrives, whether the code is accepted, whether biometrics are enabled, and whether the service expects approval on the phone or a code on another screen. A short test can prevent a much longer interruption later.
Where the experience feels less flexible
The main weakness is dependence on the surrounding RSA deployment. If I am an individual choosing an authenticator for personal accounts, I may find the app less convenient than a tool built around quick self-service setup. RSA Authenticator is not trying to be a personal vault for every login, and treating it like one can lead to disappointment.
There is also a human cost to having multiple authentication methods. More choices can be helpful, but they can also make the process harder to understand when an organization enables several options at once. A user may wonder whether to approve a request, scan a passkey, enter an OTP, or use a biometric check. The app can support these methods, but it cannot remove the need for the service owner to explain which one should be used.
Another limitation is that a phone problem can become a sign-in problem. If my device is unavailable, locked, replaced, or unable to complete the chosen method, I may need an alternate recovery route supplied by the organization. I would not assume that installing the app on a second phone automatically transfers access. Before relying on it for an important account, I would learn the official recovery process and keep any permitted backup method available.
This is a meaningful trade-off rather than a flaw unique to RSA. Stronger authentication often adds a dependency on a device or approved credential. The important point is to plan for that dependency. I would not delete the app, reset the phone, or change devices immediately before an important work trip without checking how the account will be re-enrolled.
How it compares with ordinary authenticator choices
Compared with a simple OTP authenticator, RSA Authenticator offers a wider identity experience through passkeys and biometrics, not just rotating codes. That can make it more comfortable for an organization that wants modern sign-in options alongside established OTP workflows. The trade-off is that a simple code app may feel more predictable for someone who only needs to add a handful of personal accounts.
Compared with SMS verification, the app can provide a more direct and less message-dependent path when the organization supports it. I do not have to wait for a text or search through a crowded messaging inbox. The exact convenience depends on the enabled method, but moving verification into a dedicated security app generally makes the purpose clearer.
Compared with a password manager that also stores authentication details, RSA Authenticator has a narrower focus. I would choose the password manager when my priority is organizing passwords and personal accounts in one place. I would choose RSA Authenticator when an employer or service specifically uses RSA’s identity infrastructure and expects this app to participate in the login process.
That distinction helps avoid a common mistake: choosing an app based only on the word “authenticator.” Different products may all generate codes, but they do not all belong to the same enrollment system. If an organization instructs me to use RSA Authenticator, using a different code app may not provide the passkey, biometric, or approval flow that the service expects.
Small workflow choices that make it easier to live with
One useful habit is to keep the phone’s normal unlock method working reliably before attempting biometric authentication in the app. A biometric flow is convenient, but it still depends on the device’s underlying security setup. If the phone has recently restarted or temporarily requires its primary passcode, I should be ready for that rather than assuming the fingerprint or face check will always appear.
A second tip is to distinguish an authentication request from a routine notification. When an approval prompt arrives unexpectedly, I would pause and check whether I actually started a sign-in. The convenience of approving from a phone should not turn into automatic tapping. If the request does not match something I just did, I would reject it and contact the relevant organization through a trusted channel.
A third practical insight concerns code timing. OTP codes are meant to be used promptly, so I would wait until the login page is ready before opening the code view. Copying a code too early can create unnecessary pressure if the page takes time to load or if I switch apps repeatedly. For a computer login, keeping the computer’s sign-in page visible while checking the phone is usually smoother than trying to memorize the code.
A fourth consideration is device replacement. Before moving to a new phone, I would check whether my organization requires a fresh enrollment rather than assuming the app’s installation is enough. This is particularly important for passkeys and device-bound verification, where the credential may be tied to a secure device process rather than simply stored as ordinary app content.
Who should use it, and who should look elsewhere
I think RSA Authenticator is a strong fit for employees, contractors, students, and members of organizations that already issue RSA-based sign-in instructions. It is also suitable for people who value having OTP, biometric, and passkey options available through the same authentication relationship. For these users, the app’s purpose is clear and the setup has an obvious owner when something goes wrong.
I would be more cautious if I were selecting an app for a collection of unrelated personal accounts. In that case, I would first check whether each service supports RSA Authenticator directly and whether I actually need its broader authentication model. A simpler OTP tool may be faster for a small personal setup, while a password manager may be better if I want passwords and second-factor details managed together.
The app is free to install, and its content rating is Everyone, which makes it broadly accessible as a mobile security utility. It has been available since May 24, 2011, and the current version is 4.7.1.1. The minimum operating system is 10, so I would check the phone’s software before planning an enrollment. Compatibility is especially important here because authentication tools are often needed at precisely the moment I cannot afford a setup surprise.
Its public reach is substantial, with over ten million installs, but popularity does not change the central recommendation. The average rating is 3.3 from around eighteen thousand ratings, alongside roughly twelve hundred written reviews. I read that as a sign that the experience can vary according to enrollment, organization configuration, and device circumstances. A security app may work perfectly for one managed account and feel unhelpful to someone who installed it without a clear service connection.
My verdict after looking beyond the code screen
RSA Authenticator succeeds when it is treated as part of a complete authentication workflow. Its support for passkeys, biometrics, and OTP gives organizations room to offer both familiar and newer ways to verify a user. In my experience, that makes repeated sign-ins less tedious and can be more dependable than relying on text messages or manually moving codes between apps.
Still, I would not call it the best universal authenticator for everyone. The enrollment process, recovery planning, and available methods are closely tied to the service using RSA Security. Users who want a self-contained personal tool may prefer a simpler alternative, especially if they only need OTP codes and do not want an organization-managed setup.
My final recommendation is straightforward: install it when a trusted organization tells you to use RSA Authenticator and gives you a clear enrollment path. Prepare a recovery option before changing phones, test the login soon after setup, and treat unexpected approval requests carefully. If that describes your situation, this free communication and security app can be a practical, capable part of your daily sign-in routine. If it does not, its strengths may remain locked behind a setup you do not need.
Pros
- Generates secure one-time codes for supported RSA-protected accounts.
- Works with push authentication on compatible enterprise deployments.
- Supports multiple tokens, useful for accessing several company services.
- Designed for business security and centralized enterprise authentication.
- Token credentials remain protected within the app’s secure storage.
Cons
- Primarily useful for organizations using RSA SecurID infrastructure.
- Account setup often requires an administrator or activation link.
- Some features depend on server configuration and enterprise policies.
- Changing phones may require token transfer or reactivation assistance.
- Push approvals require internet access and compatible server support.
FAQs for RSA Authenticator (SecurID)
What is RSA Authenticator (SecurID) used for?
RSA Authenticator (SecurID) is a security app used for multi-factor authentication. It generates or receives secure authentication codes that help verify your identity when signing in to company systems, VPNs, cloud services, and other protected resources. The app is generally intended for organizations using RSA SecurID technology, so it may not be useful unless your employer, school, or service administrator has provided enrollment instructions and access credentials.
How do I set up RSA Authenticator on my Android or iPhone?
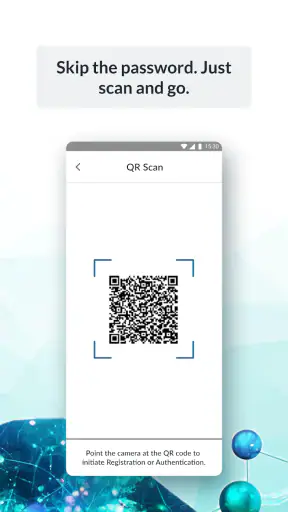
To set up RSA Authenticator, you normally need enrollment information supplied by your organization’s IT administrator. This may include a QR code, activation link, import file, or registration code. After installing the app, follow the provided instructions to register the device and create or activate your authenticator. Setup procedures can vary depending on the RSA deployment, so downloading the app alone does not usually provide access without administrator approval.
Does RSA Authenticator require an internet connection to generate authentication codes?
In many configurations, RSA Authenticator can generate time-based or event-based passcodes without a continuous internet connection once the credential has been successfully registered. However, internet access may be required during enrollment, synchronization, push authentication, or certain approval-based sign-in processes. Availability also depends on how your organization configured RSA SecurID. If codes stop working, check your device time, network connection, and contact your administrator.
What should I do if I lose my phone or delete RSA Authenticator?
If your phone is lost, stolen, replaced, or the app is accidentally removed, contact your organization’s IT or security administrator as soon as possible. They may need to disable the old credential, issue a replacement, or provide a new enrollment method. Avoid attempting to restore authentication data from unofficial backups, because security credentials may not transfer correctly and could create access or account-protection problems.
Is RSA Authenticator (SecurID) free and compatible with every account?
The RSA Authenticator app can generally be downloaded without a separate purchase, but it is not a universal authenticator for every online account. It is designed to work with systems that use RSA SecurID authentication and usually requires an organization-managed license, server, or enrollment process. Before installing, confirm that your employer, school, bank, or service specifically supports RSA SecurID and has given you the required setup instructions.

RSA Authenticator (SecurID)
This site provides independent information about third-party apps and is not affiliated with, or the owner, developer, or distributor of, any app featured here. App names, logos, and trademarks belong to their respective owners. Developer details are provided for reference; please contact the developer directly via MobileAuthenticatorFeedback@rsa.com, visit https://www.securid.com/en-us/products/one-time-password-authentication, or review their https://www.rsa.com/privacy/.